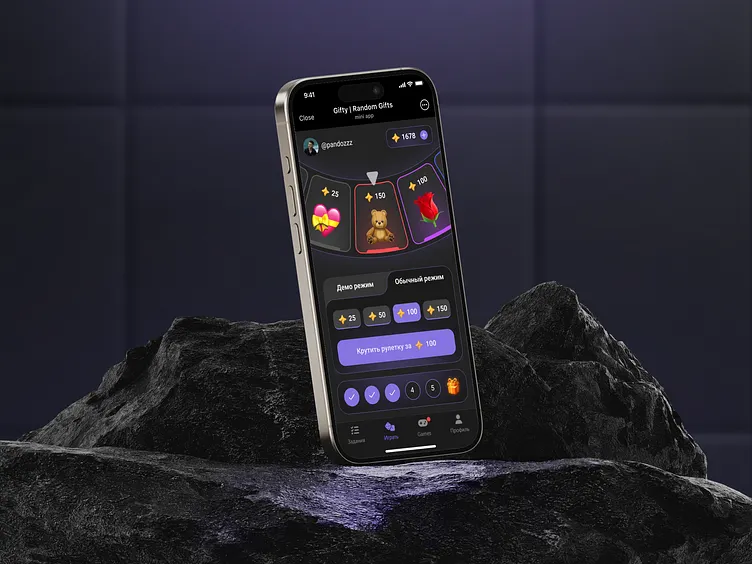
Messaging platforms have evolved beyond simple communication tools. With bots, mini applications, payment integrations, APIs, and increasingly sophisticated automation frameworks, they can serve as interfaces for a wide range of digital services. Gambling software is one area where this shift has created interesting technical possibilities, particularly for developers working on roulette products.
A roulette telegram solution is not simply a casino game embedded inside a chat application. From a software engineering perspective, it is a distributed system involving a user interface, game engine, session management, authentication, transaction processing, data storage, and often third-party integrations. Building such a system reliably requires considerably more than implementing a spinning wheel and a betting interface.
For developers, understanding the underlying architecture is therefore more useful than focusing solely on the user-facing experience.
Understanding the Core Architecture
A messaging-based roulette application can be divided into several logical layers. Although implementations differ, a typical architecture contains a client interface, application backend, game service, wallet or payment service, database, and external platform integration.
The messaging application provides the interaction layer. Users may communicate with a bot, open a mini application, or interact with buttons and menus. However, the messaging platform should generally not be responsible for the game’s core business logic.
Instead, a dedicated backend should validate requests and coordinate the application’s state.
A simplified architecture might look like this:
Client → Messaging API → Application Backend → Game Engine → Database
Additional services can handle authentication, payments, analytics, monitoring, and compliance.
This separation is important because the game engine needs to remain deterministic from the perspective of its rules while protecting sensitive operations from manipulation at the client level.
Designing the Roulette Game Engine
The game engine is the heart of the application. It should contain the rules governing bets, outcomes, payouts, limits, and round states.
One common mistake is allowing client-side code to determine the result of a spin. Even when the interface appears secure, anything calculated exclusively in the client can potentially be modified by a malicious user.
The backend should therefore control the authoritative game state.
For example, a round might move through states such as:
- Open — bets are accepted.
- Locked — no additional bets can be submitted.
- Resolved — the winning outcome has been generated.
- Settled — valid payouts have been calculated and recorded.
- Archived — the final round data is available for auditing.
This state-machine approach makes the application easier to reason about and test. It also reduces ambiguity when multiple requests arrive simultaneously.
Concurrency is particularly important. Suppose two betting requests reach the server at almost exactly the same time as a round closes. The backend must guarantee that only bets meeting the game’s timing rules are accepted.
Database transactions, optimistic locking, server-side timestamps, and idempotency mechanisms can all contribute to a robust implementation.
Randomness and Provably Fair Design
Random number generation deserves special attention in gambling software. Developers should never treat randomness as an incidental implementation detail.
A production system may use a cryptographically secure random number generator rather than a conventional pseudo-random function intended for general application development. The exact implementation depends on the regulatory environment, game design, and certification requirements.
Some platforms also use cryptographic commitment schemes to support independently verifiable results. In a simplified model, the server can commit to information before a round and later reveal the underlying value, allowing users or auditors to verify that the result was not changed retrospectively.
This type of mechanism can improve transparency, but it does not automatically make a gambling product compliant or trustworthy. Developers still need to consider how seeds are generated, protected, rotated, logged, and disclosed.
For regulated products, independent testing and certification may also be required.
API Integration With Messaging Platforms
The integration layer introduces another set of engineering considerations.
A telegram roulette application typically communicates with the messaging platform through APIs or bot infrastructure. Incoming commands or interface events are converted into backend requests, while responses are returned to the user through the platform.
Developers should treat external API calls as untrusted inputs.
Every request should be validated for:
- User identity
- Session state
- Request authenticity
- Parameter types
- Authorization
- Rate limits
- Replay protection
- Expected application state
Webhook endpoints should also be protected against forged requests. Authentication mechanisms offered by the platform should be combined with application-level authorization rather than treated as a complete security model.
The backend should never assume that a request is legitimate simply because it arrived through an expected endpoint.
Handling Wallets and Transactions
Financial transactions introduce some of the most challenging engineering problems.
A reliable wallet architecture should maintain an auditable ledger rather than relying exclusively on a mutable balance field. Each credit or debit can be represented as an immutable transaction event, while the current balance can be derived or maintained as a carefully controlled projection.
For example:
Deposit → Ledger Entry → Available Balance
and:
Bet → Debit Entry → Round Result → Settlement Entry
This approach creates a traceable history that can help developers investigate discrepancies.
Idempotency is equally important. If a network timeout causes a client to retry a transaction, the backend must recognize the duplicate request rather than processing it twice.
Unique transaction identifiers and database constraints are common tools for preventing double processing.
Payment providers should also be isolated behind a service abstraction. This allows the application to replace or add payment mechanisms without rewriting the core game logic.
Security Considerations
Security cannot be added as an afterthought to gambling software because the application handles both financial value and competitive game outcomes.
Authentication should be paired with authorization. A verified user identity does not automatically mean the user is permitted to perform every operation.
Developers should also implement server-side validation for all monetary values, bet types, game identifiers, and account actions.
Other important controls include:
- TLS for data in transit
- Secure secret management
- Database encryption where appropriate
- Rate limiting
- Audit logging
- Dependency monitoring
- Vulnerability scanning
- Administrative access controls
- Automated security testing
Sensitive credentials should never be embedded in client applications or source repositories.
Observability is another major security feature. Centralized logs, metrics, and alerts can help identify abnormal betting patterns, repeated authentication failures, API abuse, or unexpected transaction behavior.
Responsible Product Engineering
Technical quality is only one part of developing gambling software. Responsible gambling and regulatory requirements must influence the architecture from the beginning.
Depending on the jurisdiction and product model, developers may need to support age verification, geographic restrictions, account limits, self-exclusion, identity verification, transaction monitoring, and responsible-gambling messaging.
These requirements should not be implemented as isolated interface components. They need to be enforced by backend services.
For example, a user who has reached a configured betting limit should not be able to bypass that limit by switching devices, opening a new session, or sending a direct API request.
This is another reason why authoritative server-side state is essential.
Testing a Messaging-Based Casino Application
Testing should cover both conventional software behavior and gambling-specific edge cases.
Unit tests can validate payout calculations and game rules. Integration tests can verify communication between the application backend, database, payment services, and messaging APIs.
Load testing is particularly important because messaging-based applications can experience bursts of traffic. A popular promotion or major event could create thousands of requests within a short period.
Developers should test scenarios such as:
- Simultaneous bets
- Duplicate requests
- Network interruptions
- Database failures
- Delayed payment callbacks
- Expired sessions
- Invalid game states
- High request volumes
- Service restarts during settlement
Chaos and failure testing can reveal problems that ordinary functional testing misses.
The objective is not merely to prove that the application works when everything goes according to plan. It is to establish predictable behavior when individual components fail.
Monitoring and Operational Reliability
Once deployed, the platform needs continuous monitoring.
Useful metrics include API latency, failed requests, active sessions, transaction-processing time, database performance, game-round duration, and error rates.
Financial events deserve especially detailed monitoring. A discrepancy between ledger entries, balances, and game settlements should trigger investigation rather than being silently corrected.
Structured logging makes these investigations significantly easier. Each request can include a correlation ID, allowing developers to follow an event across multiple services.
For larger systems, distributed tracing can provide an even clearer picture of how a request moves through the architecture.
Where the Technology Is Heading
Messaging applications increasingly blur the distinction between communication software and application platforms. Developers can build interfaces that feel lightweight while relying on sophisticated cloud infrastructure behind the scenes.
For roulette products, this creates opportunities to experiment with conversational interfaces, real-time notifications, automated support, account dashboards, and compact application experiences.
However, the convenience of the interface should not obscure the complexity underneath. A dependable gambling application still requires strong backend engineering, secure transaction handling, reliable randomness, careful state management, comprehensive testing, and regulatory awareness.
The most effective development strategy is therefore to treat the messaging platform as an interface rather than the application itself. Core rules, financial records, authorization, and security controls should remain under the application’s direct control.
For technical teams, that architectural distinction is fundamental. Whether the product is a prototype or a large-scale commercial platform, separating presentation from authoritative business logic provides a stronger foundation for scalability, testing, security, and long-term maintenance.